Network Appliances
 Forward Proxy
Appliance
What is it?
-
This is an AWS appliance available on the AWS Marketplace here AWS Marketplace
-
Enances outboud traffic in addition to the security provided by Security Groups AWS Security Groups
-
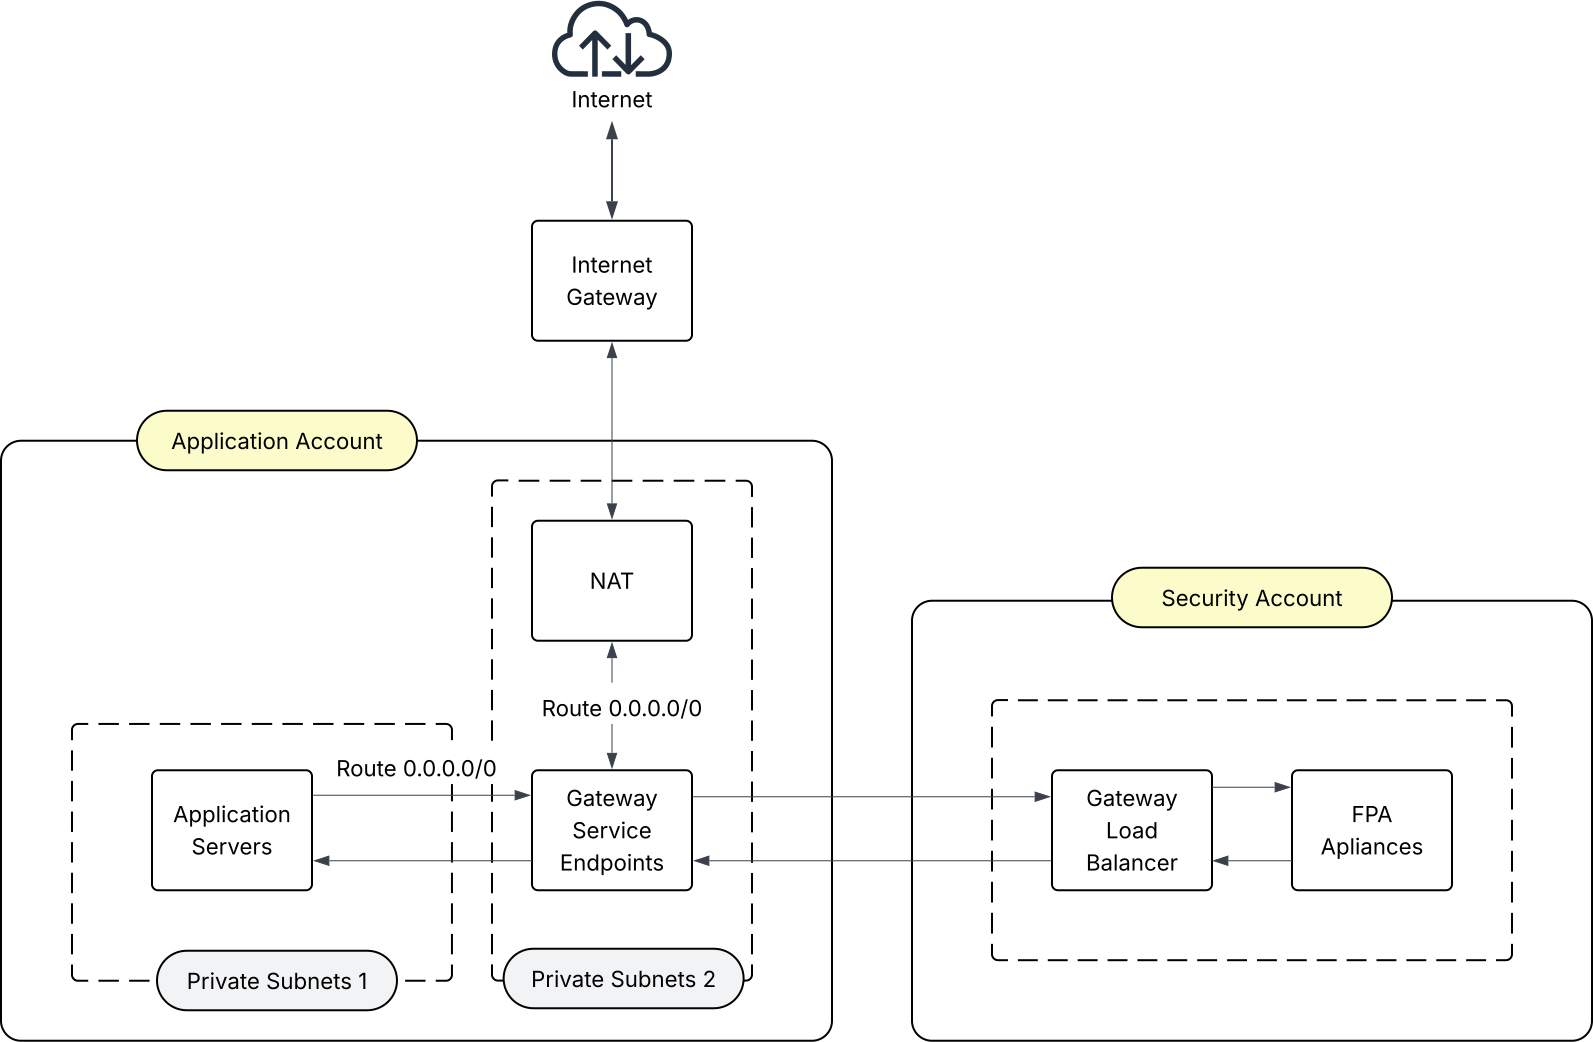
This is a forward proxy appliance that is configurable using host groups and domains in a separate security account behind a service endpoint and gateway load balancer. Instance, containers and pods are configured with metadata tags to select host profiles for internet access.
-
Each application account will have their private outbound networked appliance traffic routed through the service endpoint for filtering. The proxy is transparent.
-
The proxy is low maintenance as host profiles can be tagged or in the case of pods annotated to a specific host profile to allow access to curated list of domains.
-
When an instance, container or pod starts up for the first time a simple notification API can be used to configure the proxy to allow outbound connections. This allows for automated access based on profiles.
-
The appliances are clustered and with minimal configuration will gather configuration information across all your accounts. The cluster manages this from a single node reducing the number of AWS API requests and allowing horizontal cluster scale ability.
Why use it?
-
You want to improve your security posture by reducing your attack surface when an EC2 instance, ECS container or EKS Pod are compromised by an attacker.
-
You want an AWS aware configuration that doesn’t require manual intervention for every instance, container or pod startup.
-
You want to ensure the proxy configuration is not configurable from within your application accounts.
-
You want to be able to configure VPCs with overlapping CIDR blocks.
-
You don’t want any peering limits.
-
You want support for http as well as https.
-
You want support for different ports and transports
How is this usually addressed?
-
Block all outbound access and manually configure security group rules for a selected websites. For common site access to enable automated patching for example push access to monitoring and logging sites configure this for each specific instance type. Isolate the instances to specific security groups and manage the instances and security group mapping manually. This approach is difficult and time intensive to maintain also prone to errors.
-
Configure a security group to allow access to all outbound traffic. For a compromised instance, container or pod, this allows an attacker to phone home and orchestrate an attack on your application.
Other less commonly used approaches
-
Use Squid and manually configure each subnet and host name. This will be either too wide or require intensive amounts of labour. Most likely for EC2 Auto Scaling Groups, ECS containers and EKS pods will be difficult to maintain and will cause production issues.
-
Configure the instance firewall. If the instance is fully compromised this can be disabled by an attacker.
Basic Account Design
The appliance is run as part of a private link / endpoint service with a gateway load balancer, with multiple consumer accounts.